Your computer. Your agents. Work you can inspect.
Shadowfetch Linux is an independent Debian testing derivative with KDE Plasma 6, a creative desktop, reviewed updates and recovery tools. Version 4.0 added a native Mission Control desktop: give a task a project, choose its connection and provider, then review the files, tests and changes it produces.
Version 4.1 makes the sandbox around that work do what it already said. A declared egress allowlist is now a default-DROP nftables ruleset inside the sandbox's own network namespace; declared masked paths are real mounts; every sandbox gets a seccomp syscall filter; and names resolve inside a networked sandbox, which they did not before. It also changes behaviour that working setups depend on — a mission now has to name its provider, stored approvals stop covering missions that name destinations, and --net allow no longer reaches the host's loopback. Read the release notes before upgrading.
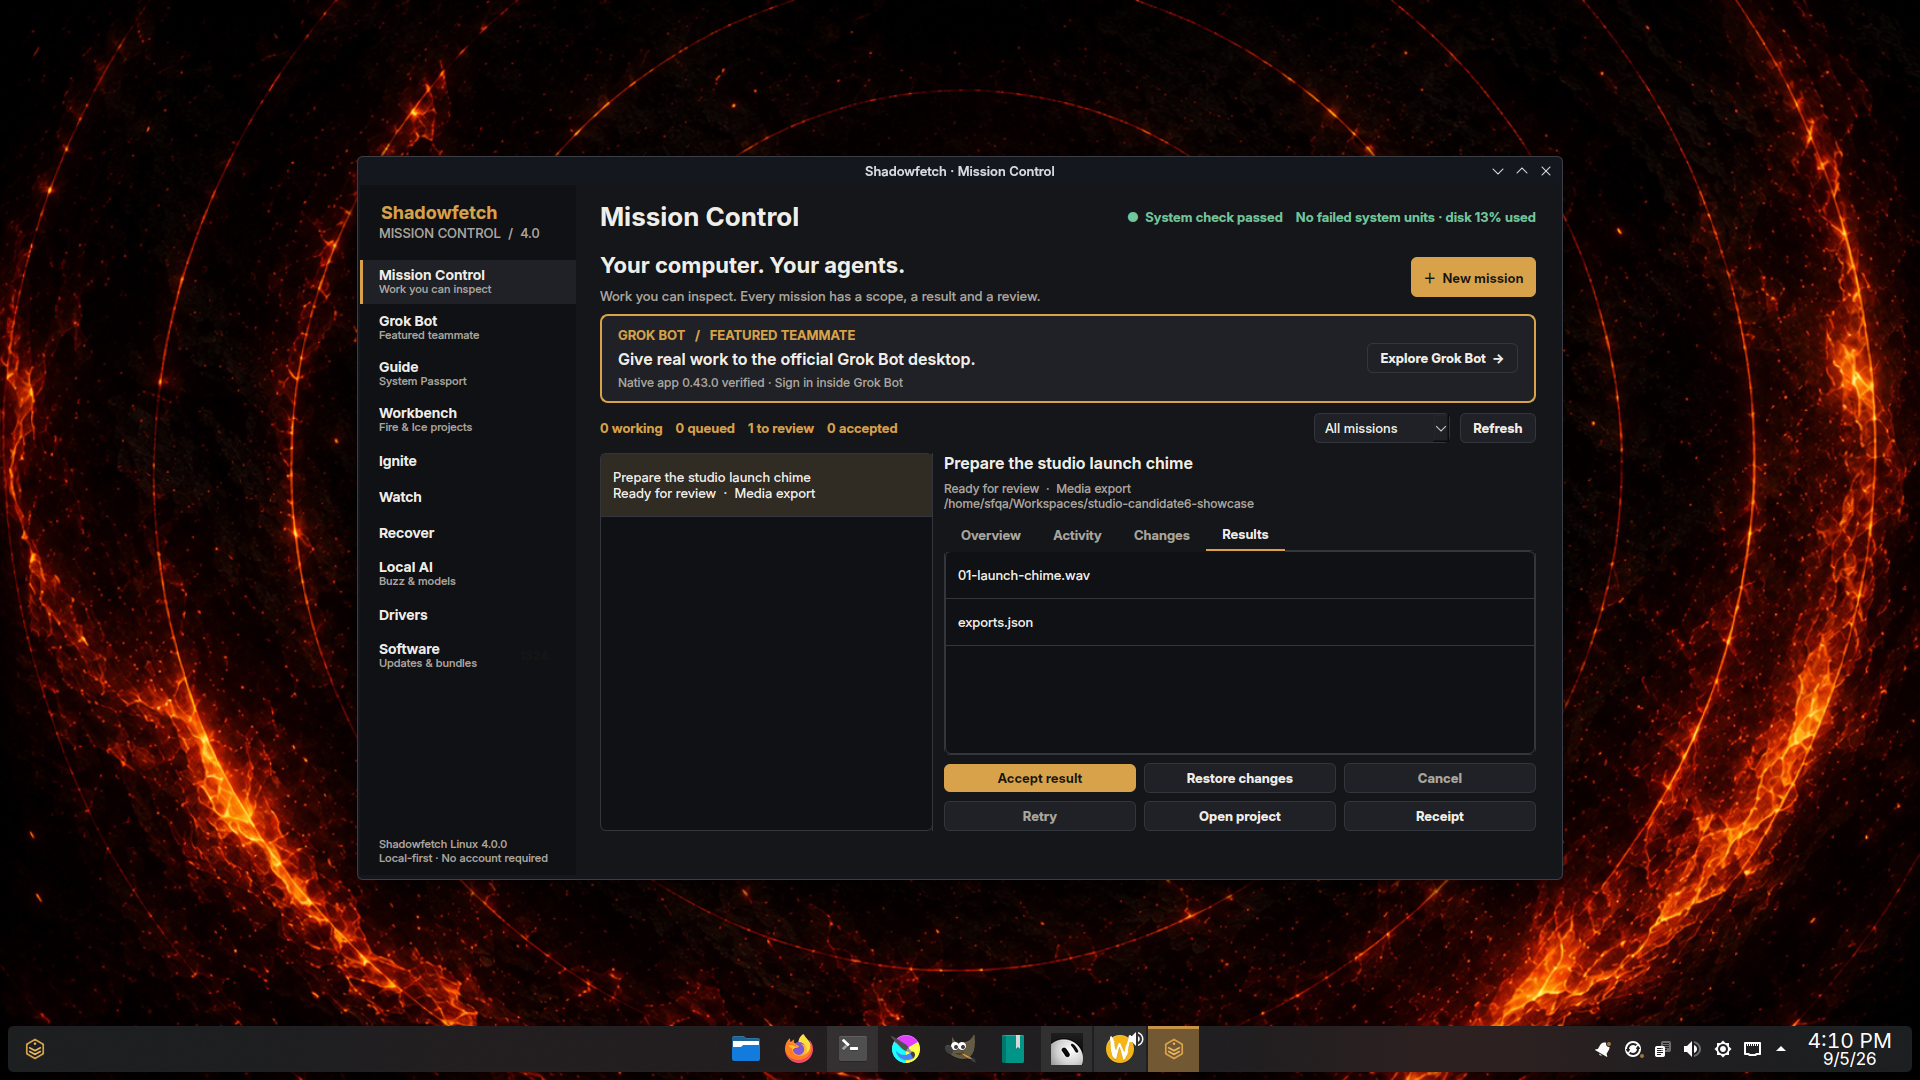
Mission Control: a persistent queue with activity, output files, diffs and review. Captured on 4.0; this interface is unchanged in 4.1, which is why the image is not recaptured. Final capture state: published (4.0 capture reused; UI unchanged in 4.1).
Official native Grok Bot. Final capture state: published on site (sign-in screen; does not prove authenticated cloud work). A launch or sign-in screen does not prove an authenticated account or a completed cloud task.
Download · Mission Control · Grok Bot · Screenshots · Release notes
| Fact | Value |
|---|---|
| Version / codename | 4.1.0 / Umbra |
| Publication date / channel | 2026-09-10 / stable |
| ISO | shadowfetch-4.1.0-amd64.iso |
| Size | 3980670976 bytes — 3.98 GB (3.71 GiB) |
| SHA-256 | e19e96302f97e94d5284f8fbef181c9b0e49ca7b746afe5e66e4bc6d5c551f25 |
| ISO product source commit / tree | 78ee38ceac0ff989d596e5a5e0b97aac17c3b936 / 163b434ebbd572522c781cc92ff48f90f7fda01c |
| Base / desktop | Debian testing snapshot 20260726T000000Z / KDE Plasma 6 |
| Architecture / APT suite | amd64 / umbra |
| Final boot acceptance | hybrid BIOS+UEFI ISO published; see known-issues for Secure Boot / VM caveats |
Signing-key fingerprint: 8F13 CE15 35EE 1F4A 2916 A1F7 3C5C 900B 7BE8 0CA1.
| Feature | What you can do |
|---|---|
| Mission Control | Create work in an existing Workbench project, watch the persistent queue, inspect activity and failures, and review files, receipts and changes. Open the same form from Workbench or Dolphin. |
| Code and tests | Request a scoped change and select the exact test program and arguments. Bounded edit/test/repair attempts leave a diff and validation record. Use your configured Codex cloud provider. |
| Reports with sources | Select project text files and generate a report with citations. Review the source support for each claim. |
| Media exports | Export selected media with deterministic FFmpeg workflows; inspect stream validation, sizes and digests alongside the files. |
| Review and recovery | Successful tasks wait for review. Accept a result, cancel running work, retry failed work or restore the local checkpoint. Restore refuses conflicts with newer project edits. |
| Featured Grok Bot | Select the official native desktop in Welcome or use its dedicated Mission Control page. The verified installer discloses the download, administrator approval and vendor update source. Sign in inside the vendor app. |
| Offline workspaces | Keep project files together and use deterministic media tools without an AI provider. An on-device provider ships in 4.1; whether it RUNS depends on a model service answering on this machine. |
Grok Bot is separate from the Grok Build CLI. Codex, Claude Code, Grok Build and Cursor Agent remain independent optional coding tools with their own account setup. Grok Bot needs an eligible vendor account and plan; a model API key does not replace its native sign-in.
Welcome keeps profile descriptions in a scrollable list with fixed navigation, and every wallpaper remains reachable through a horizontal row. The Control Center health header reports failed system units; user services and application health need their own checks. A focused DrKonqi helper lets the finite login crash-pickup scan finish, including an empty scan, while retaining KDE’s per-crash reporting path and runtime guard.
Element Workbench, the creative application stack, Guide, Ember, Firewatch, Phoenix and Fireproof remain available. Fireproof simulates and rechecks updates; supported Btrfs layouts provide Phoenix snapshot recovery. Recovery depends on the snapshots and available space.
Fire exposes connected workflows. Ice starts sandboxed agent sessions without an external network and pauses Grok Bot installation and launch. Each mission presents its connection choice. Generated code, tests and media tools run in Firebreak with writes scoped to the approved project and a restricted filesystem view. Code and source-report missions require configured Codex access and explicit network approval; media exports can run offline.
Local AI is deferred for this release. The upgrade retires Shadowfetch's Buzz integration and managed relay startup while preserving user data and separately installed vendor software.
No Shadowfetch account is required to use the desktop. Model weights and provider account sessions are not bundled. Optional vendor applications retain their own network behavior, settings, licenses and account requirements.
Receipts, prompts and source material can be private. Review files before sharing them. Local restoration cannot reverse external effects from an approved network action.
The download page links the ISO, checksum and detached signature. The SBOM, package manifest and QA evidence bundle are attached to the v4.1.0 GitHub release; see RELEASE-4.1.0.md. Use the exact accepted filename below. These commands download and verify files; they do not write a USB device.
ISO='shadowfetch-4.1.0-amd64.iso'
ARTIFACT_BASE='https://www.shadowfetch.com/linux/download'
curl --fail --location --remote-name "$ARTIFACT_BASE/$ISO"
curl --fail --location --remote-name "$ARTIFACT_BASE/$ISO.sha256"
curl --fail --location --remote-name "$ARTIFACT_BASE/$ISO.asc"
curl --fail --location --remote-name https://www.shadowfetch.com/linux/shadowfetch.gpg.asc
gpg --show-keys --with-fingerprint shadowfetch.gpg.asc
# Compare the fingerprint with the value above before importing.
gpg --import shadowfetch.gpg.asc
gpg --verify "$ISO.asc" "$ISO"
sha256sum --check "$ISO.sha256"
Continue only after the signature and checksum both verify. A GPG warning about personal key trust differs from a failed signature. Write the verified ISO with a USB image writer, then follow the installation guide.
The live session uses shadow / shadow with passwordless sudo. The installer creates the chosen user and removes the live account. See the verification guide, Secure Boot guide and known issues.
Use a 64-bit Intel/AMD computer. Plan for 8 GB RAM and 100 GB disk space for a comfortable desktop; demanding creative projects need additional memory and storage. These planning figures are not a physical-hardware certification.
Secure Boot has no Microsoft-trusted shim. Intel/AMD use Mesa; NVIDIA setup is an explicit, simulate-first workflow. VM rendering tests do not establish physical NVIDIA, AMD or Intel acceleration performance, and hybrid laptops need their own validation. Phoenix Points require a supported Btrfs root; ext4 does not provide the same snapshot recovery. Debian testing can change faster than Debian stable.
The SBOM (sbom-4.1.0.cdx.json), package manifest (packages-4.1.0.manifest) and QA evidence bundle (evidence-bundle-4.1.0.tar.gz) are attached to the v4.1.0 GitHub release. In the acceptance record, 13 cases pass, 4 are waived (Grok Bot integrity, Grok Bot screenshot, resource limits, 45-minute stress) and the publication check PUB-01 is still pending. See https://www.shadowfetchlinux.org/download and RELEASE-4.1.0.md. The release notes identify the actual install paths, graphics environment, provider tests and stress measurements.
The project uses Debian live-build, Debian source packages and a signed reprepro repository. Build on a Debian host; privileged build steps use sudo. Package builds and source tests do not require production publishing credentials.
make deps          # install build dependencies
make test          # focused behavior checks
make source-gate   # tests, parsers, linters and secret scans
make packages      # build the Debian packages into build/
The release build uses the configured signing key:
make repo          # signed local APT repository
make package-gate  # package, repository and clean-install checks
make iso           # privileged image assembly, signature and ISO gate
make qemu          # launch the resulting image for a smoke test
make iso produces shadowfetch-4.1.0-amd64.iso in the repository root. VERSION ?= 4.1.0 and CODENAME ?= umbra live in the Makefile. Signing and publishing require the maintainer's private key and authorized publisher credentials, which are not in this repository. Consult make help, the release notes and FINAL_OPERATIONS_CHECKLIST.md before release operations; .github/CI-SECRETS.md records that the CI pipeline holds no secrets and why.
Source map: packages/shadowfetch-missions/ contains the queue and execution engine; packages/shadowfetch-control-center/ contains the native Qt UI; packages/shadowfetch-welcome/ contains first boot; packages/shadowfetch-defaults/ supplies integration helpers; packages/shadowfetch-drkonqi-pickup/ contains the pinned KDE pickup source, correction and behavior checks. live-build/ assembles the desktop, tools/ holds gates and release tooling, and qa/4.1.0/ indexes acceptance evidence.
Use GitHub Issues for bugs, installation reports and hardware notes. Include the exact ISO and checksum result, firmware/boot mode, CPU/GPU/RAM, disk layout, the failing step and redacted shadowfetch-health --json output. For mission bugs, include the workflow, state and redacted receipt. Report security-sensitive findings through SECURITY.md.
Patches to packages, build tools, tests and documentation are welcome. Run make source-gate before submitting. Do not post password exports, private keys, tokens, private source files or unredacted account logs.
The ISO aggregates upstream packages under their respective licenses. Most Shadowfetch-authored code and packaging use GPL-3.0-or-later; see LICENSE and each package’s copyright file. The DrKonqi pickup helper’s own code and packaging use GPL-3.0-only; its compiled KDE source retains GPL-3.0-only OR LicenseRef-KDE-Accepted-GPL. The source package includes the upstream archive, signature, release key and downstream patch. Other upstream source retains its original license notices. Shadowfetch and Umbra names, marks and artwork are reserved under TRADEMARKS.md; rebrand derivative distributions. Optional vendor applications retain their own licenses and terms. Shadowfetch Linux is independent and does not imply Debian or vendor endorsement.